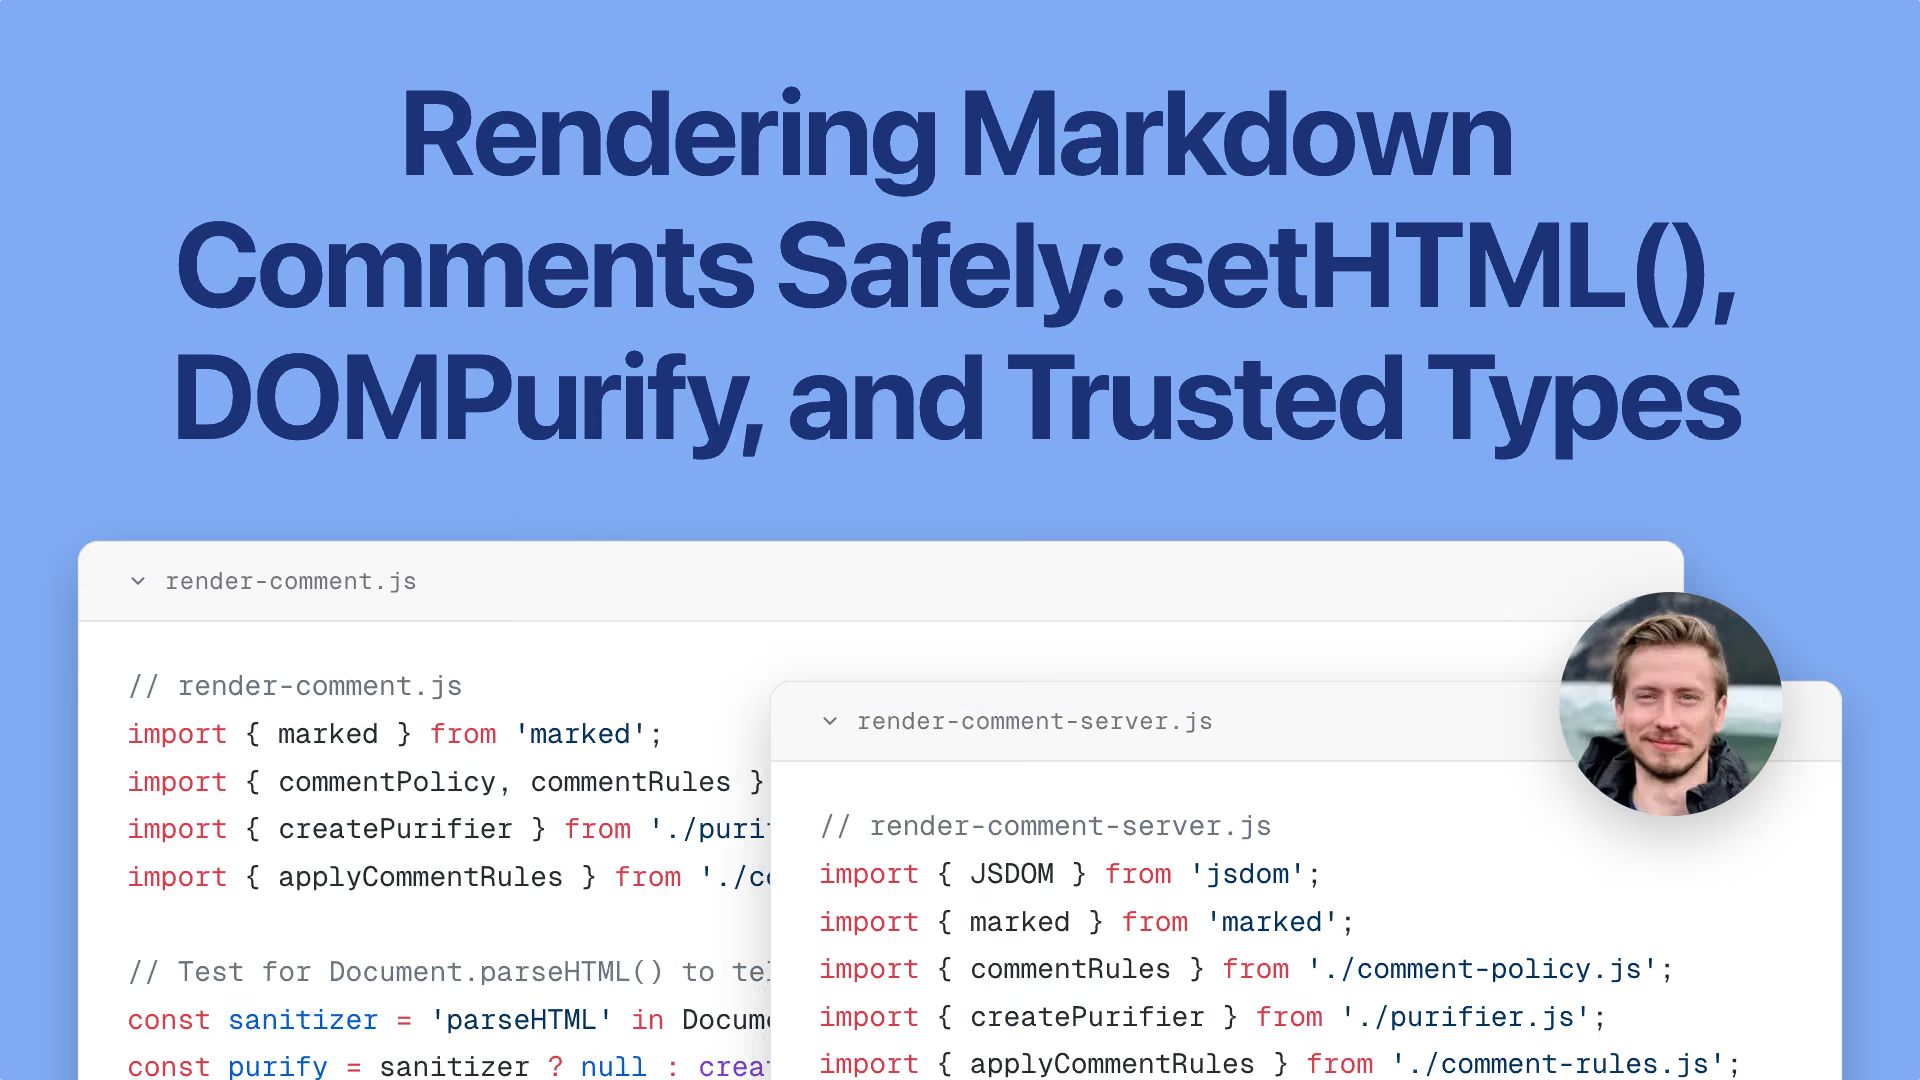
Rendering Markdown comments safely: setHTML(), DOMPurify, and Trusted Types
One explicit allowlist for every place comments render, with native and library sanitizers.

Web Standards
Daily web platform news
setHTML(), DOMPurify, and Trusted TypesOne explicit allowlist for every place comments render, with native and library sanitizers.

Seven quick wins against supply chain attacks, most doable in under a day.

A proposed API to store big files by hash and share them across origins.
A platform-agnostic reference of features every quality website should have.
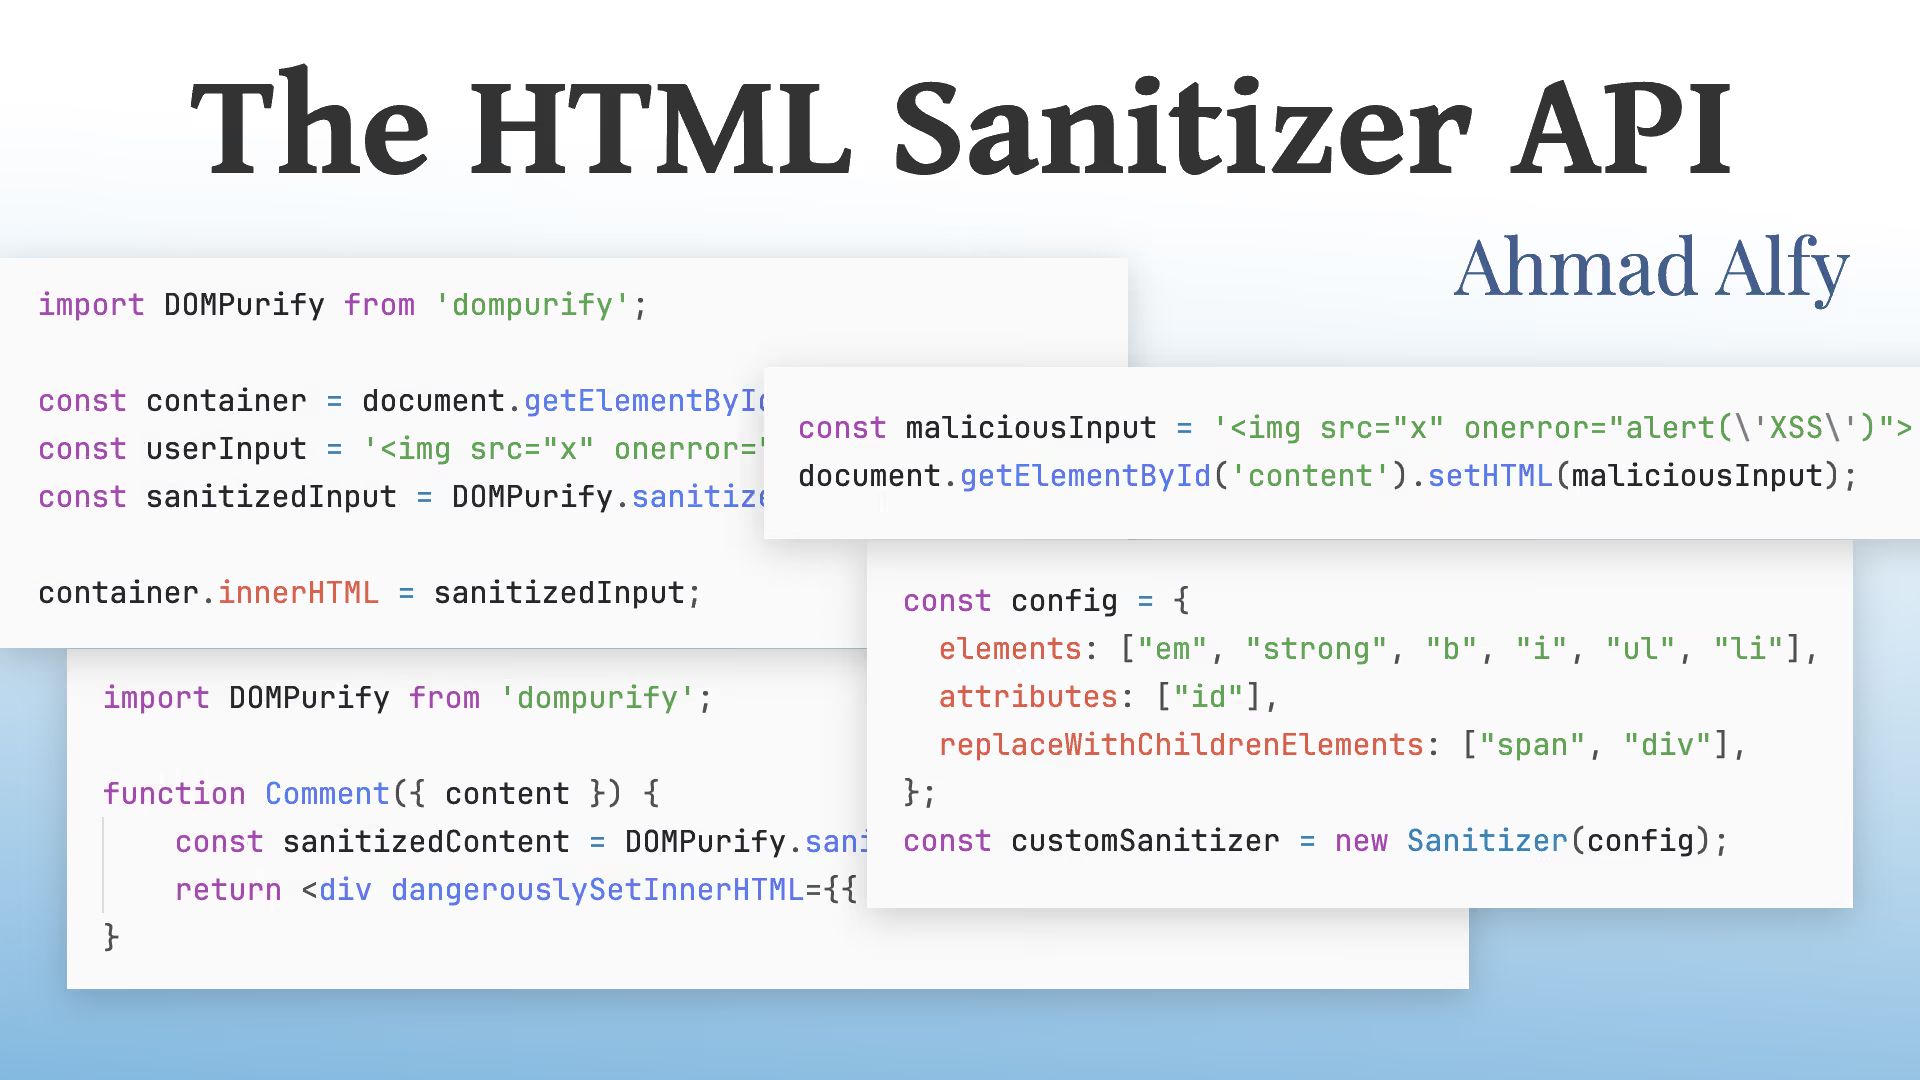
Browser-native XSS-safe HTML insertion without DOMPurify or other libraries.

setHTML(), Trusted Types and the Sanitizer APINew setHTML() and Sanitizer API prevent XSS by safely inserting HTML into the DOM.